Detection pipeline
Captured packet information is converted into model-ready features and passed to a trained Random Forest classifier. Normal traffic is recorded and released, while suspicious classifications enter the response path.
An AI-assisted intrusion-detection framework that classifies network activity and connects detection to alerts and rule-based defensive actions.
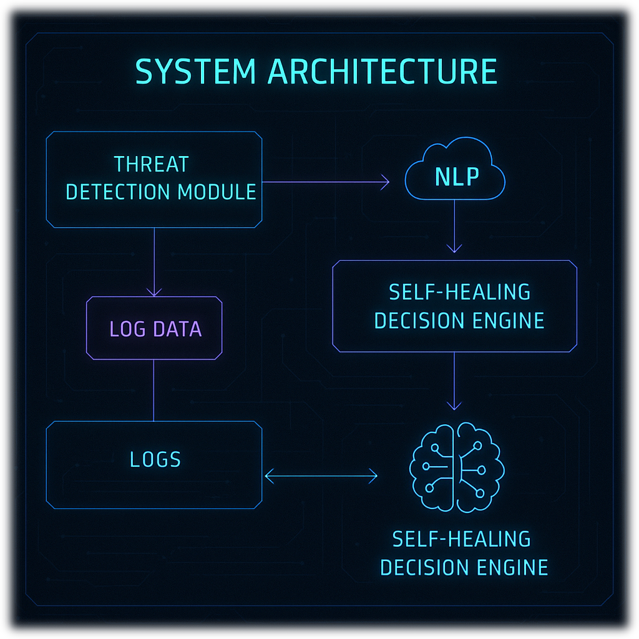
System architecture
Captured packet information is converted into model-ready features and passed to a trained Random Forest classifier. Normal traffic is recorded and released, while suspicious classifications enter the response path.
The response module maps classified attack types to transparent operating-system actions. This rule-based design keeps intervention understandable and testable while demonstrating how detection can connect to mitigation.
A Telegram bot reports attack information so that automated action does not become invisible action. The project treats timely notification and recorded evidence as part of the security workflow.